
Freeing security teams to focus on what truly matters.
Our mission
Whether you have hundreds of thousands of vulnerability reports or a few hundred, the problem is the same: no way to know which ones actually threaten the business. The result is burnout and real risk exposure. Your best people are stuck in low-leverage triage instead of applying their expertise where it matters. Attackers stay laser focused on the five paths to your critical assets. Your team should be too.
So instead of asking "which of these 100K tickets should we fix?", aisy starts with the outcomes you're protecting, whether that's preventing account takeover for high-value customers or stopping data exfiltration from core systems. We see your environment the way attackers do, connecting every asset, vulnerability, and attack chain to the threats that matter, so your team can focus on those threats.
Our story
For nearly a decade, I worked alongside enterprises like Zoom, Salesforce, and Capital One, to uncover and resolve thousands of vulnerabilities, making judgment calls on over $20 million in verified findings. The same pattern surfaced everywhere: the truly dangerous attack paths were hiding in plain sight, waiting to be chained together, while teams were buried in tickets they couldn't make sense of. The teams were capable, but they didn't have the complete picture.
We built aisy to give them that picture. We codified how attackers actually think: how they chain vulnerabilities, how they see infrastructure, and which combinations create real impact. Then we built a platform that applies that logic to your environment. You can't defend everything. But you can protect what matters if your best people have the right context to act.
Shlomie Liberow
Our Values

Think like an attacker
The way attackers work today guides what we build and which findings we flag. We stay curious about that world: we read the new research, try new techniques ourselves, and change our approach when attackers change theirs.

Start from the user
We look past the security ticket to how the user works and what they're trying to decide. Speed is how we win, so we ship early and keep improving until it's the best way to make that decision.

Make the call
We work on what matters most and say what we'd do about it. If it's easy to undo, we act without waiting for sign-off. If we're unsure, we ask early, and we change course when we learn more.

Own your work
Each of us sets a plan and sees it through. Security teams trust what we tell them, so whoever ships something can explain what they checked and what could still go wrong, whatever tools they used, AI included.
Team
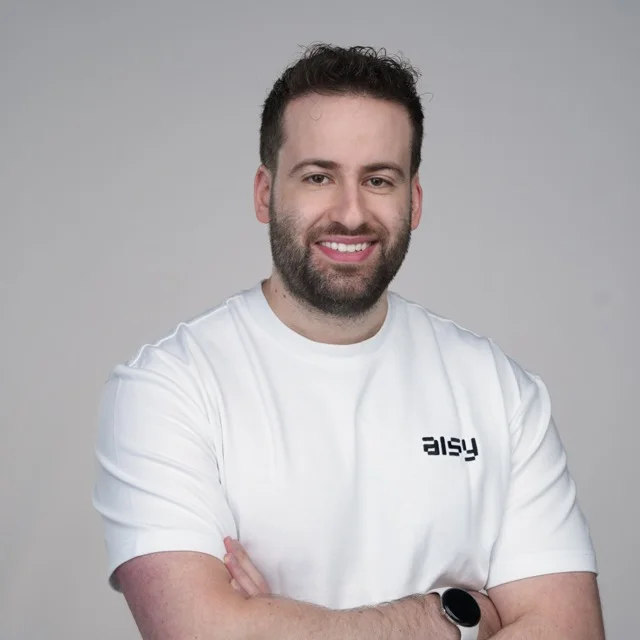
Shlomie Liberow
CEO & Founder
previously at
Aidan Matzko
Founding Engineer
previously at
Thomas Wearne
Product Lead
previously at
Jahnavee Mehta
Design Engineer
previously at